We are pleased to invite you to the 4th annual DefMal workshop, organized as part of the PEPR Cybersecurity – DefMal project.
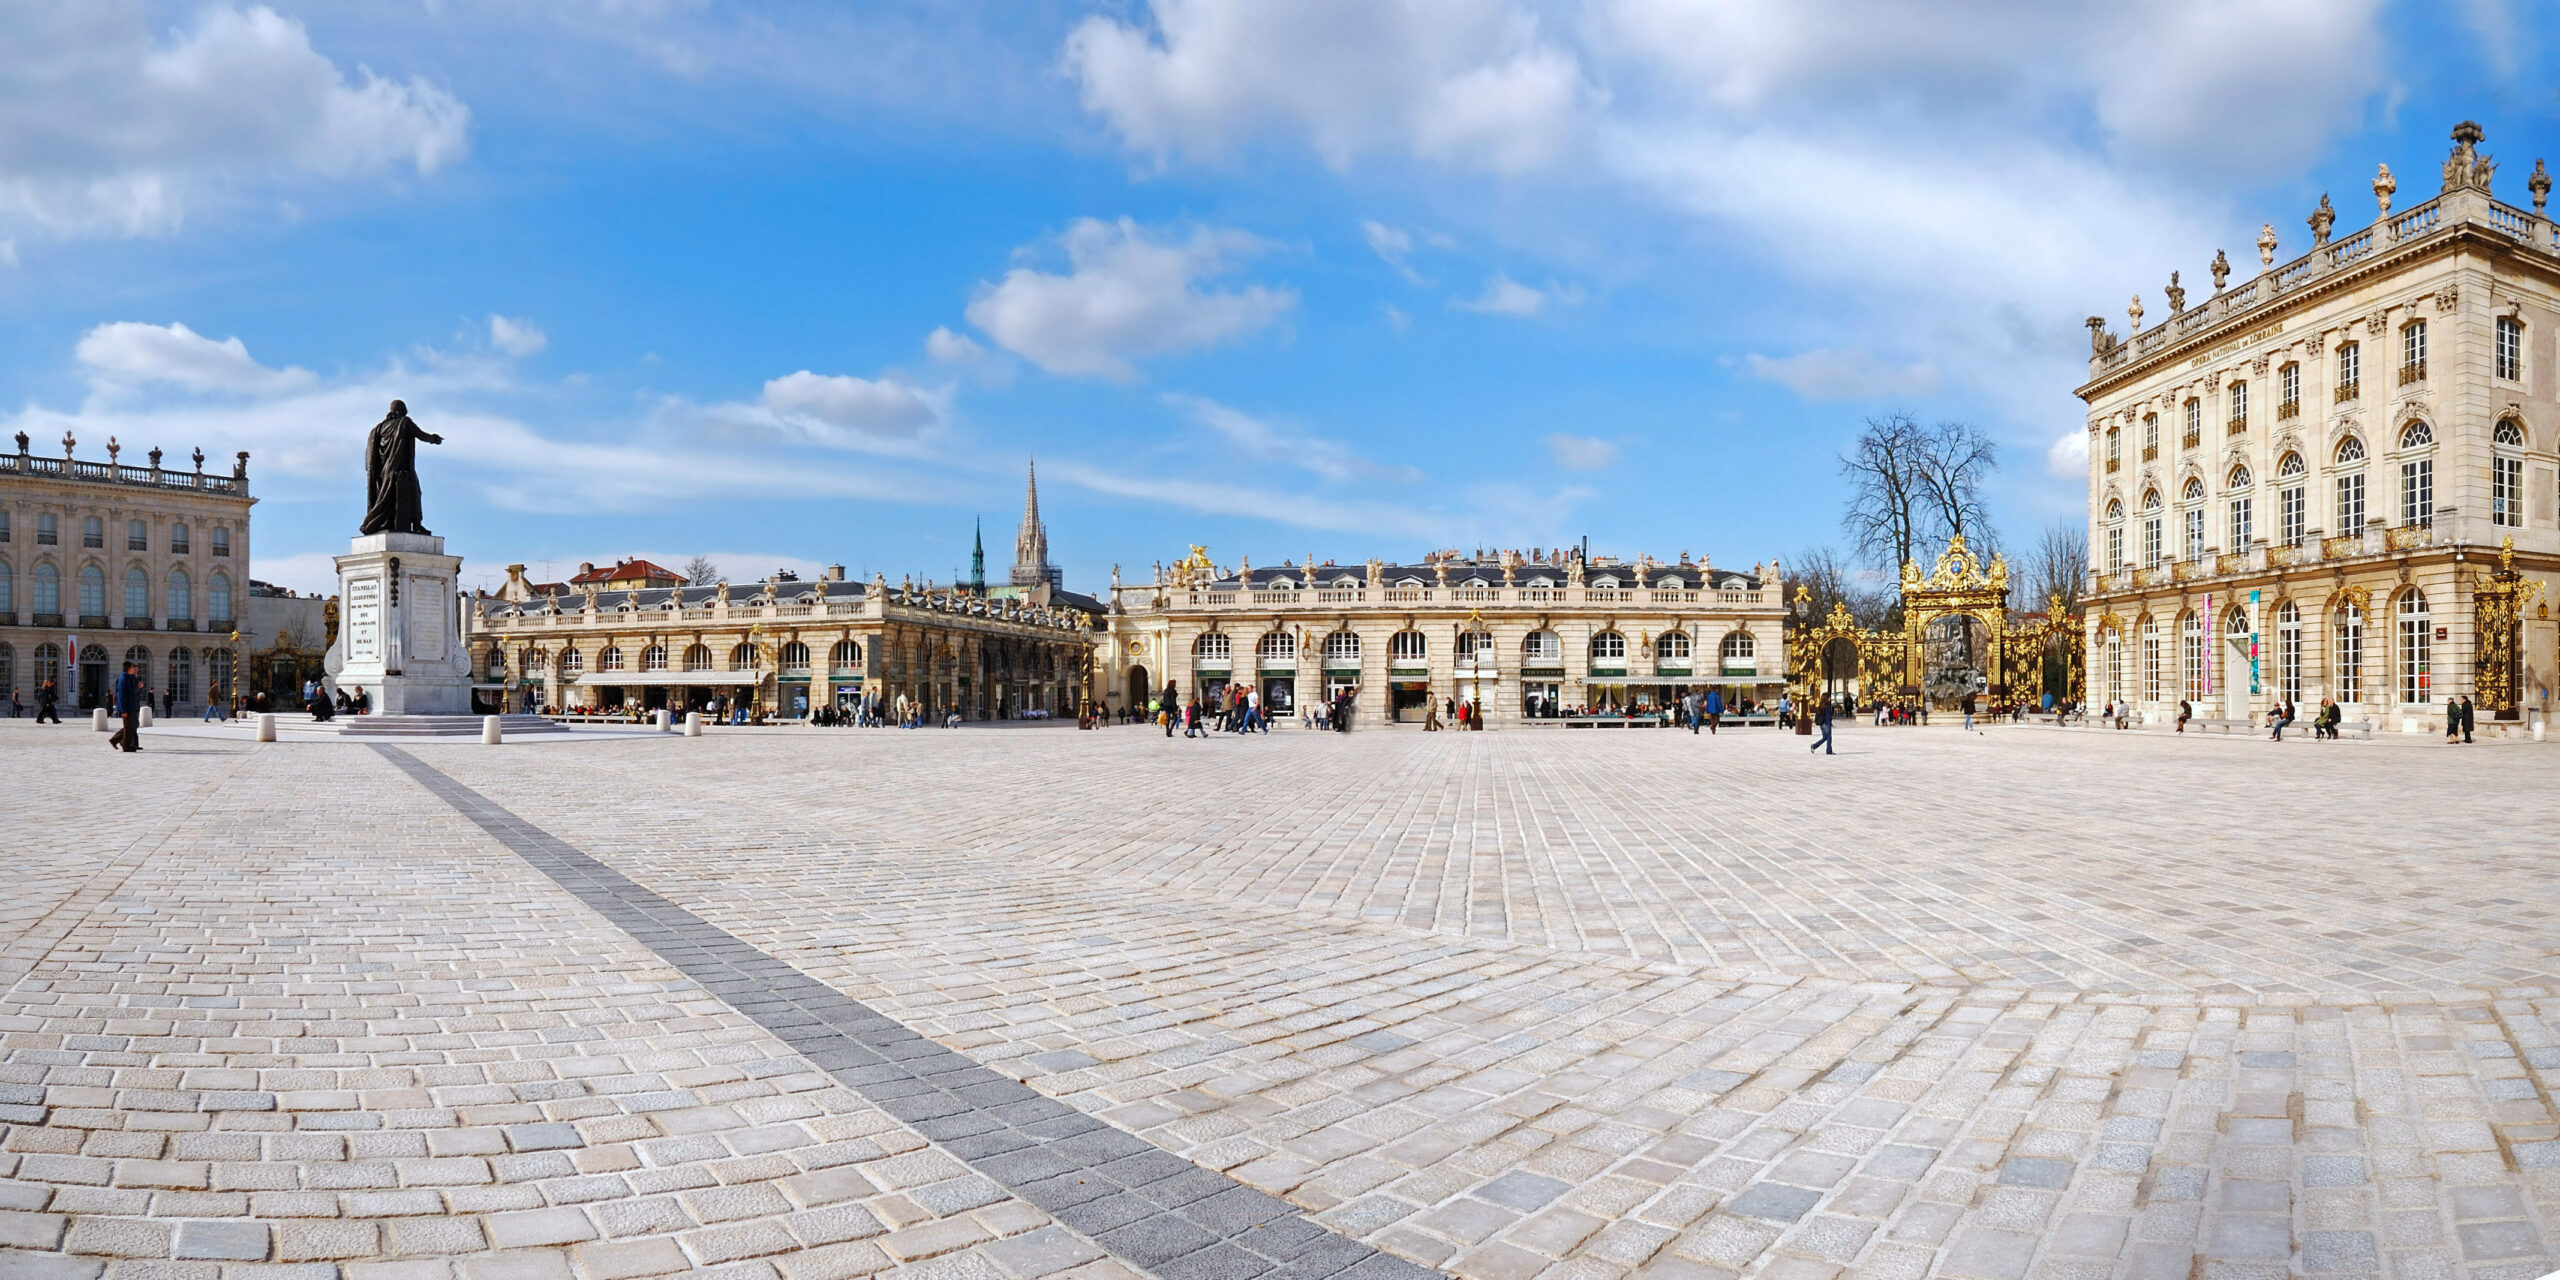
The event will take place in Nancy on October 1 -2.
This workshop is an opportunity to bring together our teams from Nancy, Rennes, Paris, and Sophia Antipolis, as well as our invited guests, to exchange ideas and share progress on our common topic: combating malware.
The program is currently under construction, and we encourage you to register as soon as possible and plan your trip accordingly.
We look forward to seeing you in Nancy!
Workshop Programme
Thursday, October 1
From 08h30: Welcome coffee
9h00 – 9h20: Workshop introduction by Jean-Yves Marion, Scientific Responsible for the DefMal and Maíra Nassau, project manager
9h20 – 10h00 : Prof. Dr. Johannes Kinder (Ludwig Maximilian University of Munich) « Robust Malware Detection using Logic and Machine Learning »
10h00 – 10h30: Grégoire Menguy (CEA List) « Redefining Grey-Box Deobfuscation through Context-Aware Program Synthesis, and Application to MBA»
10h30 – 11h00: Coffee break
11h30 – 12h00: Jean-Yves Marion (Université de Lorraine/LORIA) « Binomics + GoaTracer: Building a Reproducible Infrastructure for Malware Sequencing and Analysis »
12h00 – 12:25: Olzhas Zhangeldinov (CNRS/IRIF) «On Model-Checking Concurrent Self-Modifying Code »
12h30 – 14h00 : Lunch time at Room 101 at École de Mines
14h00 – 14h40 : Karolina Gorna (Télécom Paris) : « The Data Behind the Race : Rethinking How We Separate Program Inputs from Concurrency Bugs »
14h40 – 15h05: Sébastien Larinier (Université de Lorraine/LORIA) « One Engine, Many Brands: Ecosystem, Evasion and the Parental-Control Boundary in Commercial Android Stalkerware»
15h05 – 15h30: André Pacteau (EURECOM) « Signatures Strike Back or Fall Short? A Comparative Study of Signatures and Machine Learning for Static Malware Classification »
15h25 – 15h50: Sébastien Killian (CentraleSupélec/IRISA) « Benchmarking Progress and Reasoning in Autonomous LLM Penetration Testing»
15h50 – 16h15 : Coffee break
16h30 – 16h55: Stefano De Rosa (EURECOM) «Under the Radar: Effectiveness and Prevalence of Action-Hiding and Origin-Hiding Evasion Techniques in Windows Malware »
16h55 – 17h20 : Bassirou Badiane (CentraleSupélec/IRISA) « From Commands to TTPs: A Deterministic Approach for Large-Scale SSH Botnet Analysis »
19h00: Dinner together at Brasserie Excelsior – 50 rue Henri Poincaré 54000 Nancy, France.
Friday, October 2
From 08h30- Welcome coffee
9h00 – 9h50: Invited speaker – Prof. Dr. Alexandre Bartel (Umeå University) «Benign-Looking Code Changes for Software Supply Chain Attacks »
09h50 – 10h15: Marwa Essalehi (CentraleSupelec/IRISA) – « A Source-Derived Ground Truth and Neurosymbolic Approach to LLM-Based TTP Prediction »
10h15 – 10h40: Léo Bertrand (Université de Lorraine/LORIA) – « A Hybrid Architecture for Offensive Security AI Agents »
10h40-11h10: Coffee break
11h10 – 11h35: Maíra Nassau & Romain Guitienne (Université de Lorraine) – « DarkGoat: A Tool for Cybercrime Research and Analysis »
11h35 – 12h00: Dorian Bachelot (CentraleSupelec/IRISA) – « HYPERDRIFT: A new approach to high interaction honeypot data analysis applied to React2Shell »
12h00 – 12h25 : Victor Matrat (Université de Lorraine) – « When AI Confuses Syntax with Semantics: Functional Adversarial Examples Against Binary Similarity Models »
12h30 – 14h00: Lunch time at Room 101 at École de Mines
14h00 – 14h40: Giorgia di Pietro (Sapienza University of Rome) «1001 Malware Nights: How Malware Evades Analysis Across the Stack »
14h40 – 15h05: Flash Presentation Session – 5 minutes
– Leonard Prince (CentraleSupelec) – « Development and integration of analysis services for a malware processing pipeline »
– Lucas Villaume (Université de Lorraine) – « Hybrid anomaly detection system using artificial intelligence and formal methods »
– Sarra Djebour (CEA-List) – « Grey-box Reverse Engenering with Explanatory Queries »
-Atieh Atieh (CentraleSupelec) – « Application of Graph Foundation Models in Cybersecurity »
15h10 : Conclusions
Practical Information
Venue
The workshop will take place at Mines Nancy – Campus ARTEM,
92 rue du Sergent Blandan, 54000 Nancy, France.
Getting to Nancy
From Luxembourg Airport (LUX)
- Take the airport shuttle or bus to Luxembourg Central Station (Gare de Luxembourg).
- From there, direct trains to Nancy run regularly and take approximately 1 hour 30 minutes.
From Paris Charles de Gaulle Airport (CDG)
There are two convenient options:
- Direct TGV connection: Take the TGV from Charles de Gaulle Airport (Terminal 2) to Lorraine TGV, then the shuttle bus to Nancy.
- Via Paris: Take the RER B to Gare du Nord, transfer to Gare de l’Est, and then take a TGV to Nancy.
From Paris Orly Airport (ORY)
- Take the metro or OrlyVal/RER connection to Gare de l’Est.
- From Gare de l’Est, take a direct TGV to Nancy (travel time approximately 1 hour 30 minutes).
By train
Nancy is served by frequent high-speed trains:
- Paris → Nancy: 1 h 30
- Luxembourg → Nancy: 1 h 30
- Strasbourg → Nancy: 1 h 15
From Nancy railway station to Mines Nancy
From Nancy Ville railway station:
- Take the Tempo T1 trolleybus towards Vandœuvre CHU Brabois and get off at Campus ARTEM (or ARTEM – Blandan – Thermal, depending on the service), or
- Take Bus 11 towards Vandœuvre Roberval and get off at ARTEM. The journey takes about 10–15 minutes.